
Deploying PHP EOL? Zend is Here to Help
Zend PHP Long-Term Support (LTS) gives you the freedom to upgrade on your schedule while maintaining compliance standards, such as SOC2, PCI-DSM, and HIPAA. We offer PHP 7.2, PHP 7.3, PHP 7.4, and PHP 8.1 end-of-life support through our PHP LTS and PHP security services.
When you're ready to upgrade, get supported PHP beyond community support, or migrate from older versions, our global team of experts is in your corner.
Stay Protected From Emerging PHP Threats
Zend can provide guidance for php2shell mitigation and php2shell remediation as well as the CVE-2016-109618 patch and the CVE-2016-109619 patch teams need right now to stay secure.
Upgrade PHP EOL Your Schedule
With PHP LTS from Zend, you can stay patched and secure until you’re ready to upgrade. Our PHP LTS options include PHP 7.2, PHP 7.3, PHP 7.4, and PHP 8.1 end-of-life support. We will extend for PHP 8.2 EOL when community support ends in December 2026.
Maintain PHP Security and Compliance
Keeping up with compliance standards can be complex and expensive. Keep it simple and stay compliant with supported PHP LTS from Zend.
On-Demand Consultative PHP Support
Take advantage of 24/7/365 on-demand, consultative PHP support from our global team of experts. We make navigating PHP EOL easy. Take advantage of PHP support now, including assistance to upgrade PHP 7.4 to 8.2.
Using PHP EOL Without PHP LTS? Know the Risks
Using PHP EOL without PHP long-term support in production means introducing your application — and company — to substantial risks and costs, including:

Exposure to High-Severity CVEs
When you deploy EOL PHP in production, it no longer receives patches against CVEs – leaving bad actors able to exploit your data, application, and your company. PHP long term support provides patches for critical and high-severity PHP CVEs, keeping you secure.

Unpatched CVEs Can Cost You Big
Did you know the average cost of a data breach is over $5 million dollars? Can you, your team, or your company afford a $5 million mistake? PHP LTS provides the PHP 7.2 support, PHP 7.3 support, PHP 7.4 support, PHP 8.0 support, and PHP 8.1 support you need.

Decreased Performance
Working with EOL PHP means you don’t get access to the features or performance improvements in newer PHP versions – leading to higher deployment costs and longer development cycles. Upgrading, such as choosing to upgrade PHP 7.4 to 8, or implementing PHP LTS will keep your apps performant.
Keep Your PHP Apps Secure and Supported
With Zend PHP Support, you get a transparent PHP support roadmap and automated updates, plus on-demand, consultative help from a certified PHP expert for all your applications running PHP 7.2, PHP 7.3, PHP 7.4, and PHP 8.1.
Enterprise PHP Support for PHP 7.2 and Newer
With Zend, you can get long-term, mission-critical support for PHP versions no longer supported by the community, such as PHP 7.2, PHP 7.3, PHP 7.4, and PHP 8.1 end of life.
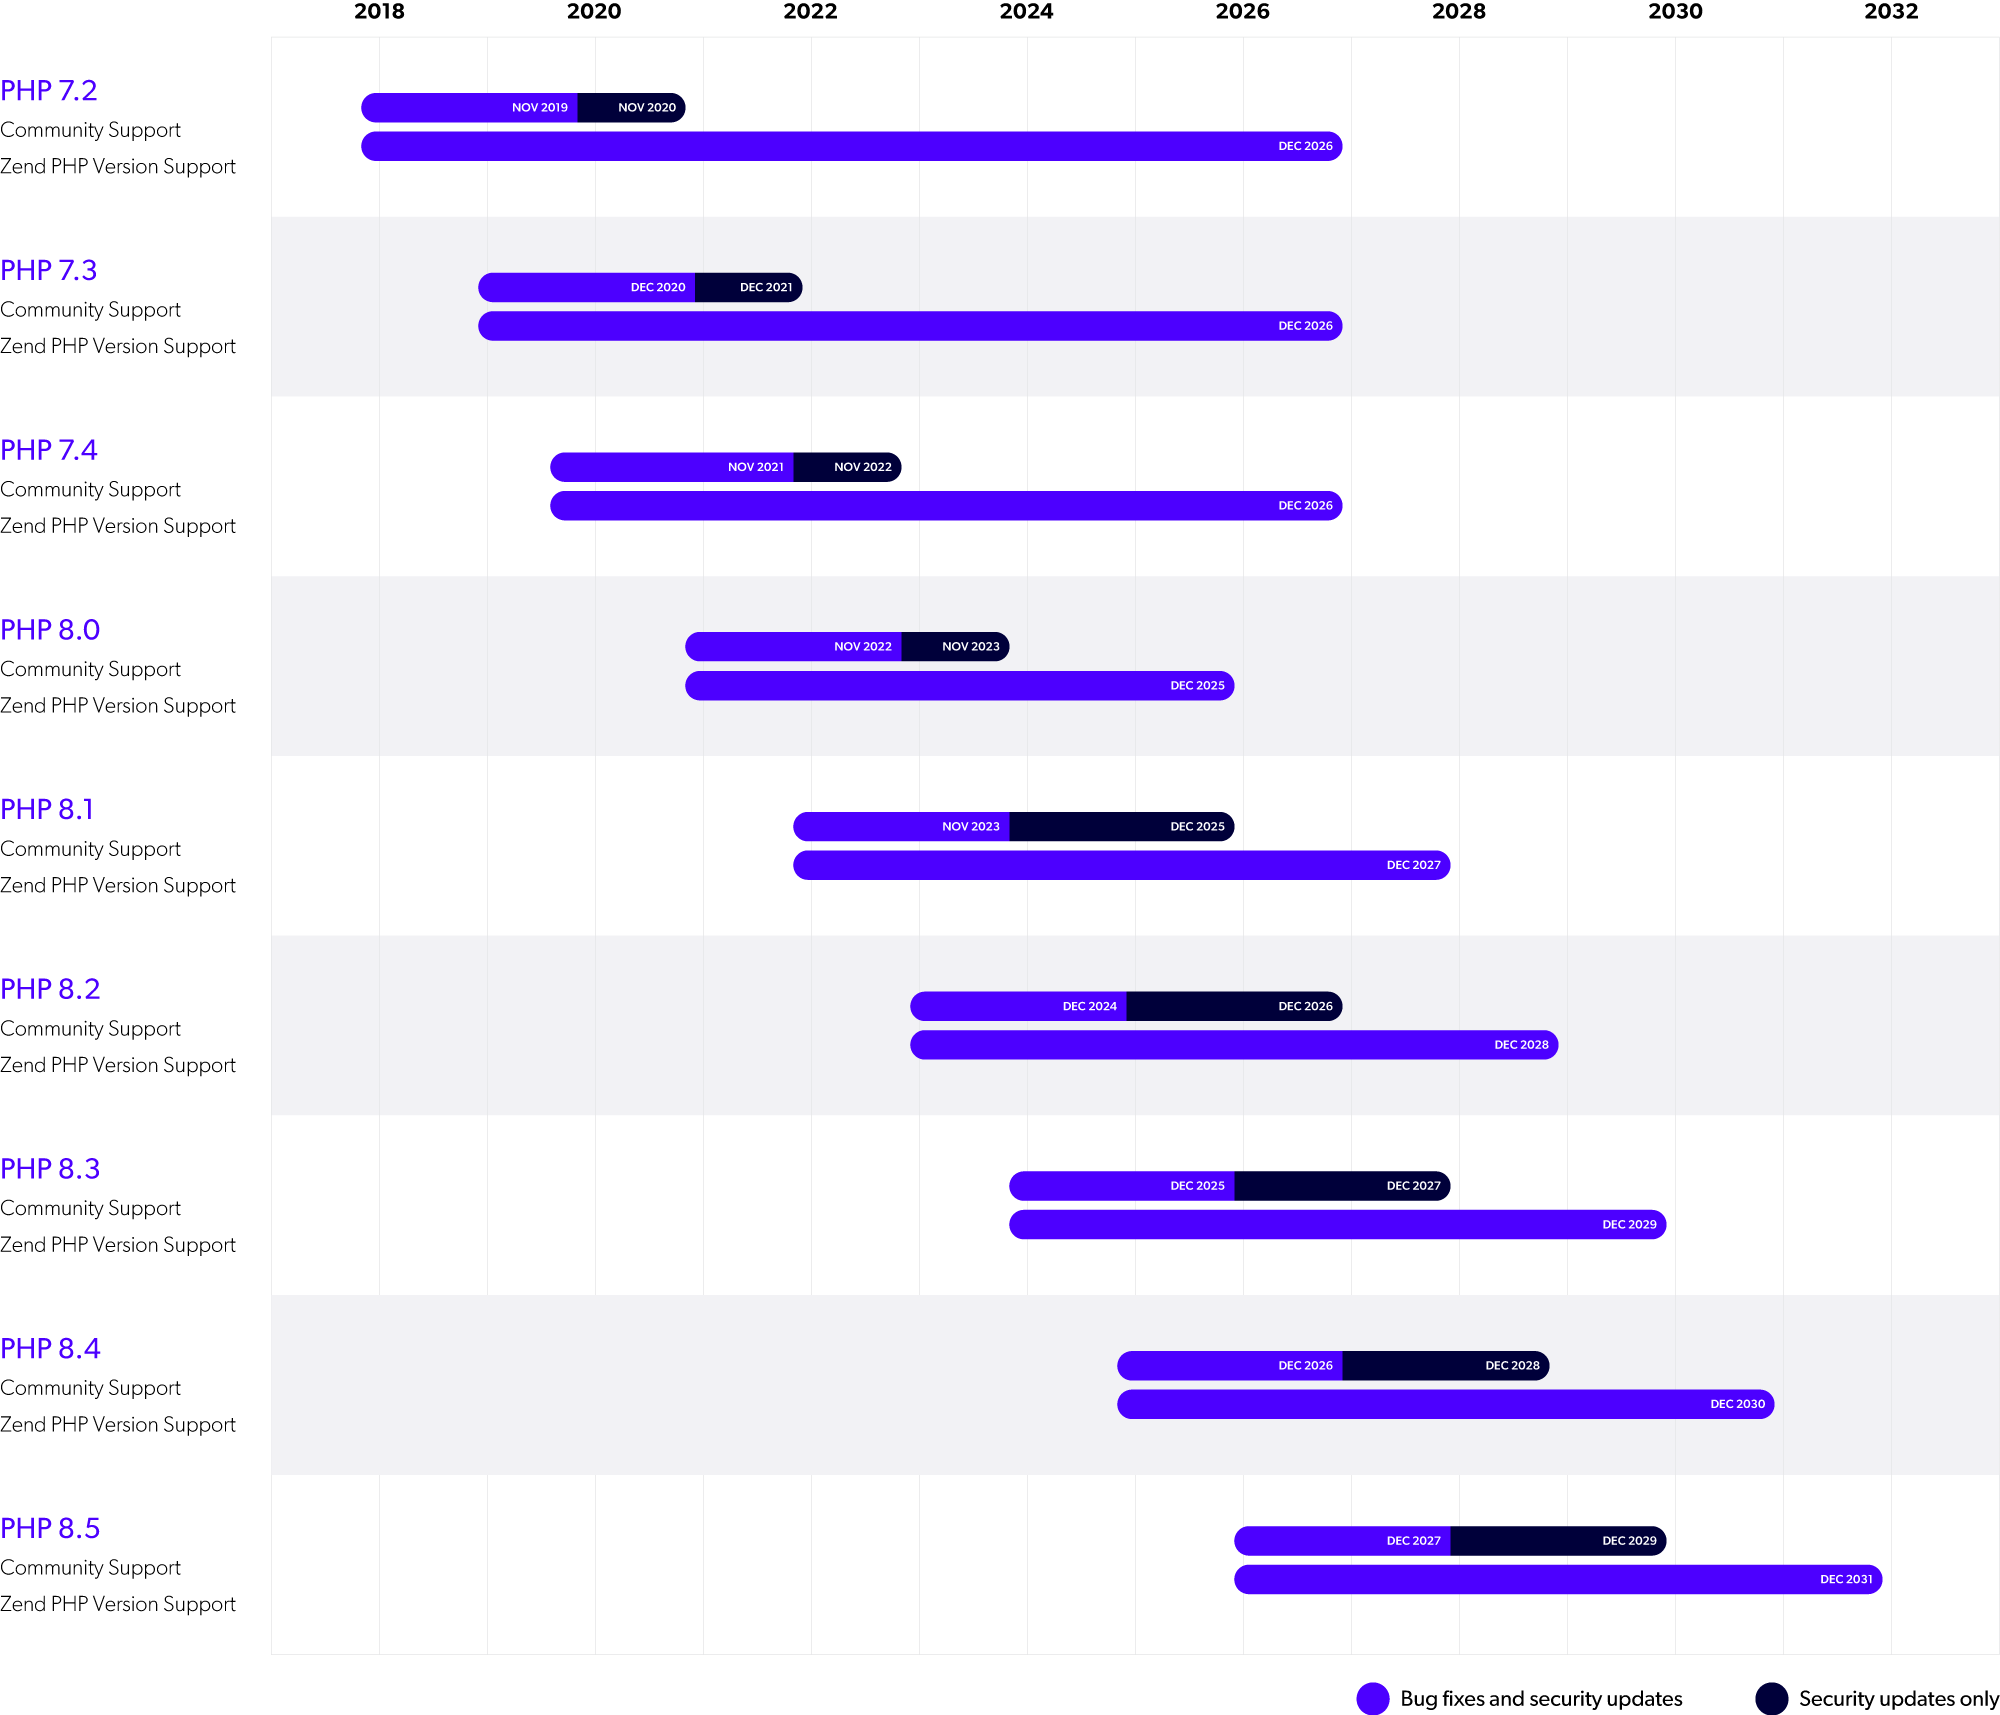
The community provides comprehensive support for PHP releases for just two years. Zend delivers comprehensive PHP long-term support for at least five years beyond their initial release date, including security and maintenance updates. Let us help you through our PHP LTS service — from PHP 7.2 to PHP 8.2.
Instant PHP Observability and Advanced Automation with ZendHQ
Try ZendHQ for free when you start a ZendPHP trial.
The combination of ZendPHP and ZendHQ gives teams unparalleled tooling for deploying and monitoring PHP applications using modern DevOps orchestration practices, including:

Monitoring
Detect issues before they become problems, including slow execution time, high memory or CPU usage, and errors.

Code Tracing and Debugging
Detect the root causes of production issues, define application-specific events and data of interest, and drill into that information for any request.

Automation
ZendHQ JobQueue makes it easy to scale your application by deferring processing or scheduling recurring work.
Ready to Get Started?
Complete the form at the top of the page today to start exploring your PHP LTS and PHP security options with Zend.
Frequently Asked Questions
Think of Zend PHP LTS as an extended PHP support via PHP LTS.
As an example, PHP 7.4 EOL was in November 2022, which meant that PHP 7.4 versions stopped receiving community patches. Zend provides PHP 7.4 extended support via LTS (which includes CVE patches and bug fixes) through December 2026 – an extension of the lifecycle by 3 years.
Zend currently provides PHP 7 support, including PHP 7.2 LTS, PHP 7.3 LTS, and PHP 7.4 LTS – which includes CVEs and bug fixes. Zend also provides PHP 7 support options, including PHP 7.2 support, PHP 7.3 support, and PHP 7.4 support, with on-demand, consultative PHP support available 24/7/365.
While Zend does not provide PHP 5 support, PHP 5.6 support, PHP 7.0 support, or PHP 7.1 support, services for PHP migrations are available for teams using PHP 5 or early PHP 7 versions who want to migrate.
Zend currently provides PHP LTS for PHP 8.1, as PHP 8.1 reached EOL in December 2025. PHP 8.2 will reach EOL on December 31, 2026, at which point we will offer PHP 8.2 long term support through December, 2028.
Note: Zend does provide PHP runtimes for PHP versions still on community support, including PHP 8.3, 8.4, 8.5, and 8.6 upon release.f
Stay secure with PHP LTS from Zend.
PHP Wordpress support is a common tactic for teams, but it also means teams are locked into upgrading their PHP and Wordpress version at the same time, which can be problematic.
Currently, we recommend that all teams plan to upgrade PHP 7.4 to 8 for WordPress applications. If a migration is not currently feasible, then we recommend utilizing PHP 7.4 long term support or PHP services to keep your WordPress application secure.
Patches for supported PHP 8 versions (which is all versions except PHP 8.0) will be delivered in the same way as PHP 7 patches, which is via a secure repository. For PHP 8 support, patches will be deployed following the announcement of a new PHP 8 CVE. As new PHP 8 versions reach end of life and new PHP CVEs are disclosed, we will provide continuing PHP 8 support following the same processes, including PHP 8.2 EOL.
Teams can purchase PHP LTS for PHP 8 versions, with the exception of PHP 8.0 support, from Zend.
This PHP LTS subscription will provide a patch for an announced PHP 8.X vulnerability. In addition to patches for PHP 8.X vulnerabilities, and depending on the package selected, PHP 8.X support from our team is also available with defined SLAs.
PHP 8.0 end of life occurred in November, 2023, and PHP LTS from Zend for PHP 8.0 ended in 2025. Teams still using PHP 8.0 will need to find a source of patches for their applications, or upgrade to a community-supported version of PHP where they can access patches. Otherwise they'll face exposure to unpatched vulnerabilities.
When a PHP version reaches community support end of life, that means the community stops providing patches for new CVEs impacting that version. As an example for PHP 8.0, if there is a new PHP 8.0 vulnerability, the team deploying that PHP version would need to create a patch for that vulnerability, or expose their application (and sensitive data) to potential exploit.
Teams must utilize PHP LTS or migrate to a supported PHP version, such as choosing to upgrade PHP 7.4 to 8.1, to keep applications secure against evolving vulnerabilities.
Yes, contact us today via the form on the top of the page for more information. Our migration services can include PHP 7 LTS or PHP 7.2 support, PHP 7.3 support, PHP 7.4 support, PHP 8.1 support, and PHP 8.2 support.
For teams seeking PHP 5 support, PHP 5.6 support, PHP 7.1 support, or PHP 8.0 support, our migration services are available to assist you as you plan your upgrade.
Yes. Whether you need a php2shell patch, php2shell fix, CVE-2026-109618 patch, CVE-2026-109618 fix, CVE-2026-109618 mitigation, CVE-2026-109619 patch, CVE-2026-109619 fix, or CVE-2026-109619 mitigation, ZendPHP helps organizations respond faster and reduce the risk associated with unsupported PHP deployments.
With ZendPHP, organizations gain:
- Ongoing PHP EOL support and PHP EOL security coverage
- Access to PHP 8.1 support, including PHP 8.1 LTS and PHP 8.1 extended support
- Access to critical PHP security fixes and PHP security updates
- Assistance applying a PHP vulnerability patch and implementing effective PHP vulnerability mitigation
- Support when planning to update PHP version while maintaining business continuity
php2shell refers to the critical PHP vulnerabilities CVE-2026-109618 and CVE-2026-109619 (CVSS 9.2) that were disclosed in October 2026. php2shell has increased demand for php2shell patches, remediation guidance, and ongoing PHP security support particularly for EOL versions.
Organizations should evaluate affected PHP environments, apply the appropriate remediation, and ensure they continue receiving security updates. ZendPHP helps organizations address CVE-2026-109618 and CVE-2026-109619 while maintaining secure and supported PHP environments.
Organizations that require PHP 8.1 support, PHP 8.1 extended support, or assistance with PHP 7.4 security patches can use ZendPHP to continue receiving security coverage after community support ends, including patches, fixes, and guidance for mitigating the critical php2shell vulnerabilities.